Measured. Not attested.
Essential 8 that stays evidenced.
ACSC-aligned cybersecurity maturity for Brisbane businesses. Measured monthly by our platform — not attested annually by a consultant’s spreadsheet. Two clear paths, published pricing, and evidence you can hand to an insurer, auditor or procurement officer on demand.
Same measurement. Choose whether we stop at the roadmap or execute it.
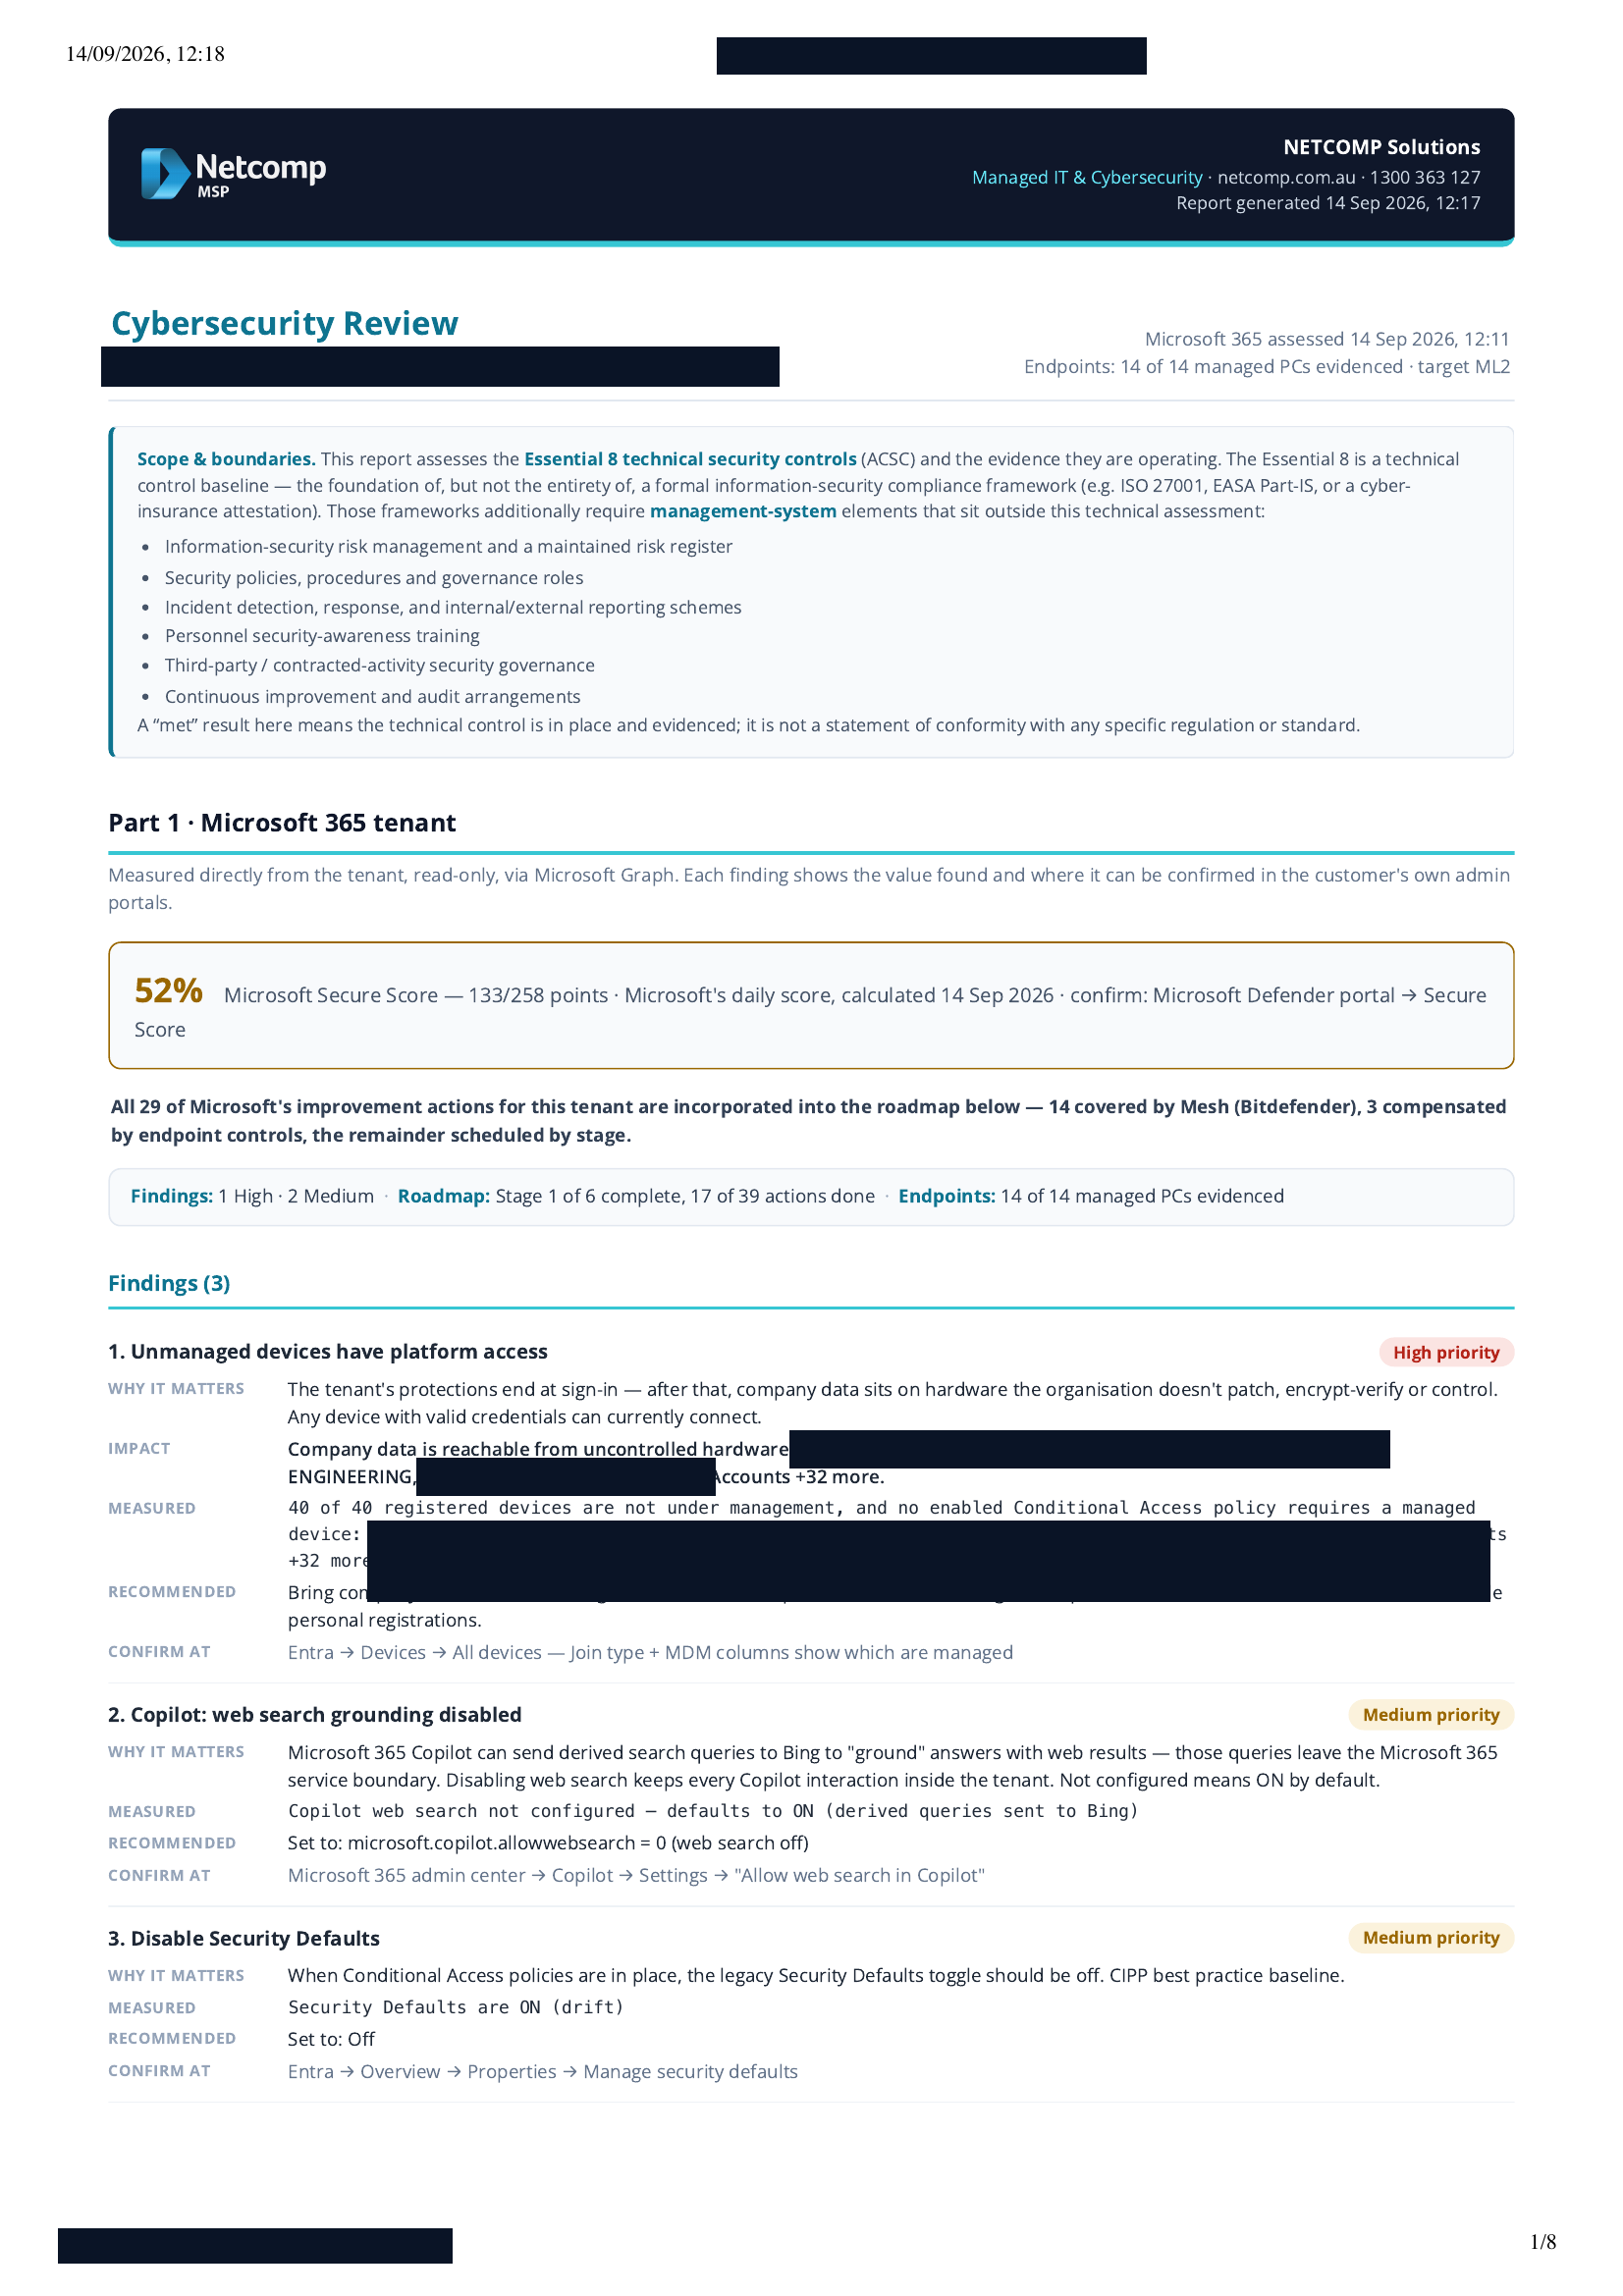
Every engagement starts with the same read of your Microsoft 365 environment against the Essential 8. What differs is how far you want us to go — hand the roadmap to your own team, or have us execute the tenant-side remediation and keep the maturity in place with monthly evidence.
We assess, execute, and keep it evidenced.
Everything in Path B, plus tenant-side remediation and full onboarding onto continuous ML1/ML2 with monthly evidence.
EVERYTHING IN PATH B, PLUS
- Full endpoint scoping (not just M365 tenant)
- Execution of tenant-side remediation: external sharing lockdown, guest access controls, admin role reduction, MFA enforcement, account lockout policy
- Post-remediation verification report showing what closed against the baseline
- Continuous ML1 or ML2 posture with self-healing controls
- Monthly re-issuable evidence report — hand to insurer, auditor or procurement on demand
- Full managed IT support included at the same monthly fee
The read and the roadmap. Your team does the rest.
One-off assessment of your Microsoft 365 environment. Suitable for businesses with capable internal IT or an existing MSP that will execute the remediation themselves.
WHAT YOU GET
- Point-in-time maturity score against ML1 or ML2 (your target)
- Evidence pack showing current posture across all 8 controls
- Prioritised remediation roadmap your team can execute
- Independent second opinion on your existing MSP's work
- Documented findings suitable for board or insurer submission
All prices in AUD and include GST.
Three forces converging on Australian SMBs in 2026.
Essential 8 is no longer optional for a growing set of Australian businesses — even though there's no single piece of legislation naming it.
DISP mandate (November 2025)
Every member of the Defence Industry Security Program now requires Maturity Level 2 across all 8 controls. That's dragging the rest of the supply chain with it — customers in DISP-aligned procurement now push the same evidence requirements to their vendors.
Cyber insurance underwriting
Australian cyber insurers now routinely require Essential 8 evidence — particularly MFA coverage and patching cadence — and price accordingly. Policies increasingly exclude losses on unsupported operating systems entirely.
Procurement questionnaires
Larger Australian customers now include Essential 8 maturity self-attestation in vendor questionnaires. Being asked to self-attest without evidence to back the claim is a legal and reputational risk your smaller clients hand back to you.
Measured every day, not attested once a year.
Most Essential 8 assessments produce a PDF. Ours produces a live evidence layer. Every control that can be verified from telemetry is checked daily against your Microsoft 365 tenant and every managed endpoint — and where it drifts, our platform puts protective settings back automatically.
The compliance report re-issues on demand: an insurer asks for current MFA coverage, we press a button. A procurement officer wants to see your patch cadence, same thing. No "we'll do a quarterly review and get back to you."
The distinction matters most at renewal time. Competitors sell you a certificate — a snapshot of a moment. We sell you a state, maintained.
What actually changes between maturity levels.
The ACSC's full maturity matrix runs dozens of pages. This is the summary a decision-maker needs.
| Control | Maturity Level 1 | Maturity Level 2 |
|---|---|---|
| Application Control | User profiles + temp directories | All workstations + servers, ASD block rules |
| Patch Applications | Internet-facing in 1 month, others 1 month | Internet-facing in 48 hrs, weekly vulnerability scans |
| Configure Office Macros | Blocked from internet origin | Trusted location and vetted publisher required |
| User Application Hardening | Flash, Java, ads blocked | + PowerShell logging, .NET v3.5 disabled |
| Restrict Admin Privileges | Separate privileged accounts | + Privileged Access Workstations, credentials not cached |
| Patch Operating Systems | Internet-facing in 1 month | Internet-facing in 48 hrs, weekly scans, unsupported OS removed |
| Multi-Factor Authentication | All remote access + privileged actions | Phishing-resistant MFA for privileged accounts (FIDO2/certificate) |
| Regular Backups | Performed + offsite retention | + Quarterly coordinated restore test, immutable retention |
Most Brisbane SMBs need ML1 as a baseline. ML2 becomes relevant if you sell into DISP, hold government clients, or have cyber insurance that references it. ML3 is rare outside government and critical infrastructure. Whatever you target, the ACSC's guidance is unambiguous: all eight controls at the same level, or your exposure defaults to the lowest one.
Essential 8 across regulated and compliance-sensitive sectors.
Three formal Essential 8 reports delivered with prioritised remediation roadmaps and evidence packs — plus three further clients at the technical implementation stage.
Aviation design organisation
Delivered gap analysis, tenant remediation and continuous evidence pack — used as the technical component of the client's regulatory information-security submission.
Industrial equipment operator
Essential 8 evidence pack integrated with existing operational tooling, mapped to insurance and customer procurement requirements. Ongoing monthly evidence via Managed Secure.
Metals & manufacturing SMB
Assessment against ML1 baseline with prioritised uplift to close highest-value findings. Continuous evidence retained via ongoing managed service.
Frequently asked questions
Find out where you actually sit.
A free 30-minute audit against the Essential 8. No obligation, no sales script — just an honest read of your posture and which path makes sense.